Phishing Kit Breach
Good Morning, Chat Bob is really a hassle! I was notified by F-Secure that my google account had been breached by a phishing kit:
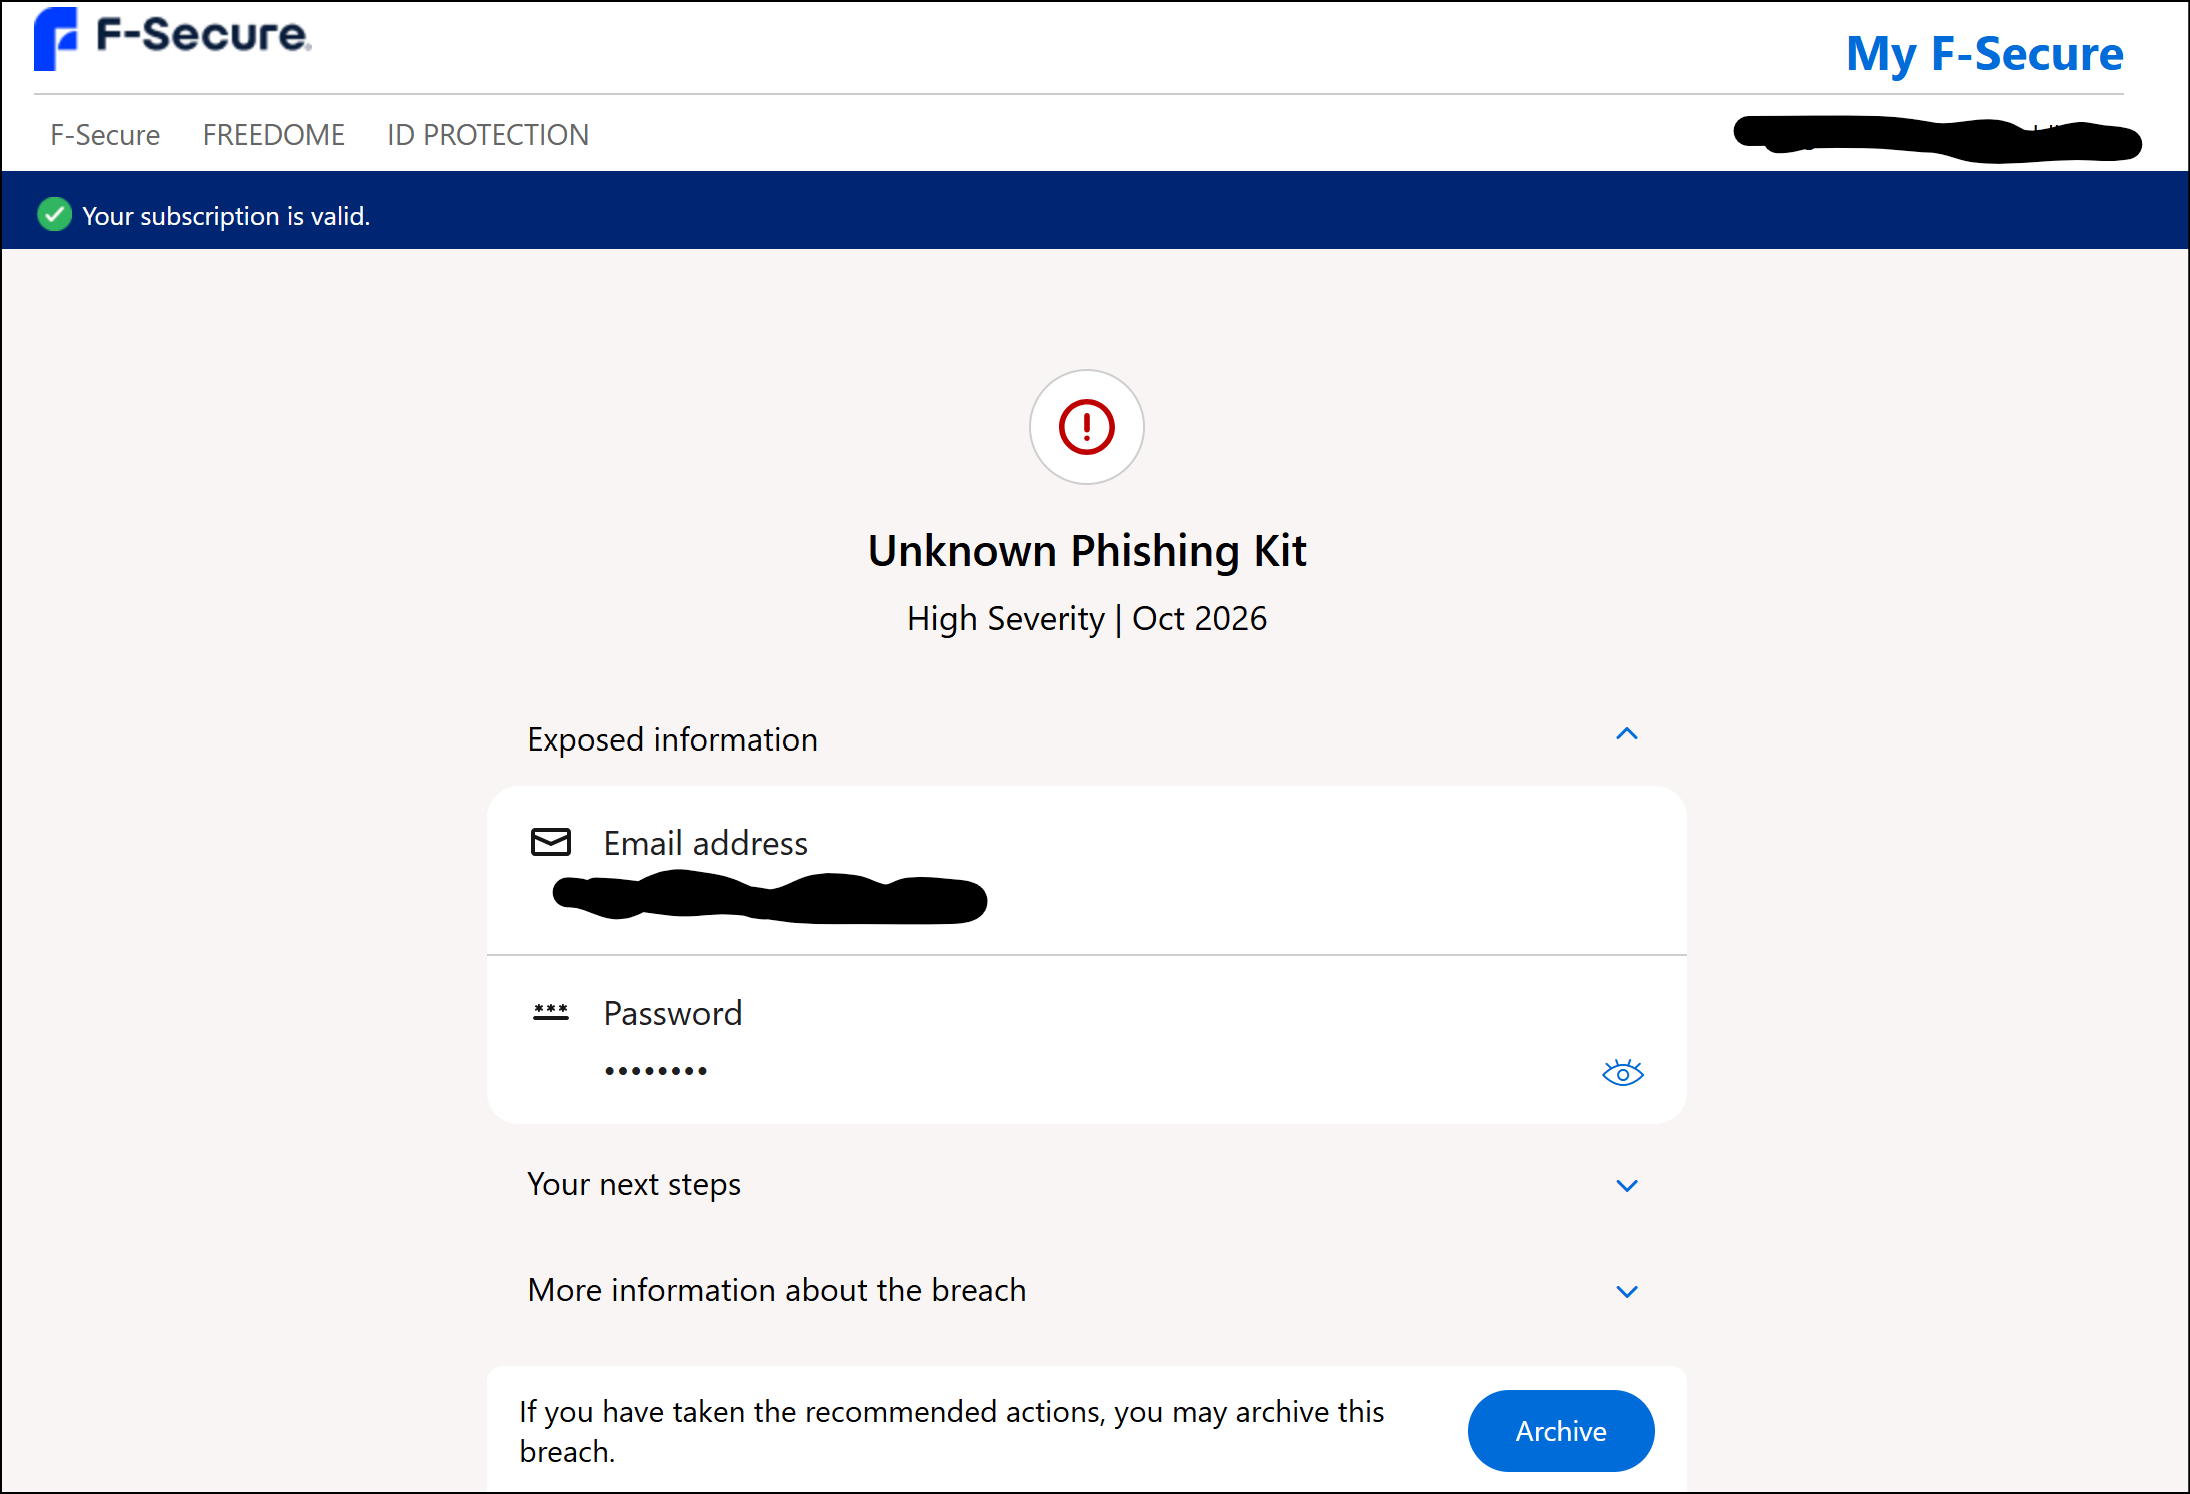
When I select the show password icon to reveal the password it is an old password. I have a new password for about 3 months now. Can you clarify whether or not my account was breached or not? Is this just a notification that the phishing kit used the old password to attempt access but didn't actually breach?
Answers
-
Hello,
I think Chatty Bob should suggest to connect you with a Support Agent if there is no way to provide any help.
Anyway, a knowledge base article on this subject is available: F-Secure ID Monitoring found a breach, what should I do? (and My personal information is available in the Dark Web or another service that was breached is not disclosed. What can I do?)
So, as per your situation:
- something monitored is found by F-Secure intelligence in some 'publicly' available place and marked as part of "Unknown Phishing Kit" source (such as the result of 'Phishing Kit' of unknown origin, source or whatever else. Perhaps, it is just a published leaked data claimed to be part of 'gathered information' with some phishing kit).
- since revealed password is the old one - then it is based on 'old' breach/leaked data or the result of malicious activity on your devices.
Now, it is not like your "Google Account" is surely hacked or breached. But somehow 'email address' with a 'password' (as a pair) gathered by whatever way. And, possible, it could have been used or set aside to be foisted on someone later, but that didn't happen because you changed your password (and 'gathered' data is invalid to use; but was valid at the time).
Is this just a notification that the phishing kit used the old password to attempt access but didn't actually breach?
Basically, it is a notification about the fact:
- your email address and 'nowOld' password (as a pair) have become known to unwanted pranksters, scammers or plain criminals at some point (where they could use this as valid credentials).
- this "situation" has just now become known to the 'hidden' public. And F-Secure found it.
- since "unknown phishing kit" is used as a name; then - perhaps - such a leak is a result of visited phishing website or webpage by opening some phishing email or any other sort of dangerous situation.
as a random thoughts: maybe it can be even some sort of infostealer or tricky browser's extension. For example, if passwords are saved in Browser in use - then it is 'hacked' from there. Otherwise, maybe you tried to type/login with them while visited fake page.
Do you recall any sort of strange situations for past three or more months?
the fact that you changed your password and 'leaked' one is old now - good.
the trouble is - what else (other accounts or passwords) are in known for potential 'malicious actors'; and where passwords were not changed. And if system is clean and safe now.
Does my reply clarify something or make situation much more obscure?
-
First, thank you for taking the time to respond! I really appreciate it.
I agree about chat bob, but getting a hold of an agent is even harder. I might end up switching providers. I been with F-Secure since 1998/9. It is sad that it is so hard to get a professional on the line for help, you can't even call in anymore. The numbers I tried provide a short message and then hangs up on you. Something like this that could be solved in 5 min over the phone takes a couple of days now! How is that progress? Don't get me wrong, f-secure is a great product, but I value good customer support. Back in the day when you had access to CS I learn so much while on the phone. Now a day's you have to do a bunch of research to source your specific issue, which there are so many similar derivatives with different solutions it is hard to nail down the right one. What was it the Major Mokoto Kusangi said, "over specialize and you breed in weakness".
I don't store passwords on my computer, even with f-secure's vault or do autofill; just not there yet. I mean every major financial institution and major government has been hacked and the people's data has been stolen 10x over. It's kind of amazing how passive communities have become.One feature I do like is the gui that pops up to tell you which sites are trust to make purchases on. It is interesting how all that is evolving.
Your response provides clarity. Thank you Ukko. Mahalo
-
Hi @Arealtaxcut
I received an email notification last week regarding an Aggregated Credential Combolist (DB-Market Update - 3) breach. It was an older server hack, as I had changed that password and all others like it, about 3-4 years ago.
And I agree, love the Scam Protection/Banking module of F-Secure :)